
HR 10671 Re-checks Congress.gov for new actions and updates the bill's status, and fills in any sponsors, committees, or related bills that are missing. It does not re-pull sponsors/cosponsors/committees/related — those rarely change — and it skips all work if nothing has changed upstream, so it's cheap to click.
Securing Our Critical Infrastructure Act
To amend the Cyber Incident Reporting for Critical Infrastructure Act of 2022 to reauthorize a program of the Cybersecurity and Infrastructure Security Agency relating to security vulnerability warnings, and for other purposes.
Summary
- Renames and reauthorizes CISA's ransomware vulnerability warning pilot program under Section 105 of the Cyber Incident Reporting for Critical Infrastructure Act of 2022 as a permanent-in-name "security vulnerability warning program," covering vulnerabilities in information systems generally rather than only ransomware.
- Requires CISA to automatically enroll each covered utility in its cyber hygiene services, with utilities able to opt out by notice to the Director.
- Requires CISA, when it determines a covered utility has been affected by a cyber incident, to use its incident response capabilities to respond on the utility's behalf, as appropriate.
- Exempts information shared under the program from disclosure under federal and state open-records and similar laws, and limits how CISA may use or disclose that information.
- Defines "covered utility" to include water or wastewater utilities serving no more than 100,000 people, eligible entities under the Infrastructure Investment and Jobs Act, and operators of public water systems or treatment works, and sets the program to terminate five years after enactment of the new subsection.
- Directs CISA to coordinate with the Environmental Protection Agency in carrying out the program.
AI-generated plain-language summary of the bill text — neutral, and may be imperfect. See the full text below for the exact wording.
Sponsor (1)
-
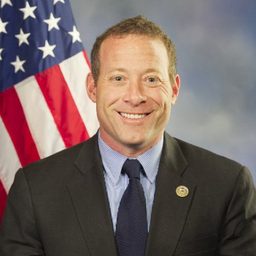 Rep. Gottheimer, Josh (D-NJ) [#5]
4 cosponsors
-
 Rep. Bacon, Don (R-NE) [#2]
-
 Rep. Landsman, Greg (D-OH) [#1]
-
 Rep. Nunn, Zachary (R-IA) [#3]
-
 Rep. Scholten, Hillary J. (D-MI) [#3]
Actions (2)
- Oct 1, 2026 Referred to the House Committee on Homeland Security. · house
- Oct 1, 2026 Introduced in House
Full text
IN THE HOUSE OF REPRESENTATIVES
October 1, 2026
Mr. Gottheimer (for himself, Mr. Bacon, Mr. Nunn of Iowa, Ms. Scholten, and Mr. Landsman) introduced the following bill; which was referred to the Committee on Homeland Security
A BILL
To amend the Cyber Incident Reporting for Critical Infrastructure Act of 2022 to reauthorize a program of the Cybersecurity and Infrastructure Security Agency relating to security vulnerability warnings, and for other purposes.
Be it enacted by the Senate and House of Representatives of the United States of America in Congress assembled,
SECTION 1. SHORT TITLE.
This Act may be cited as the “Securing Our Critical Infrastructure Act”.
SEC. 2. REAUTHORIZATION OF A PROGRAM OF THE CYBERSECURITY AND INFRASTRUCTURE SECURITY AGENCY RELATING TO SECURITY VULNERABILITY WARNINGS.
Section 105 of the Cyber Incident Reporting for Critical Infrastructure Act of 2022 (6 U.S.C. 652 note) is amended—
(1) in the heading—
(A) by striking “ransomware” and inserting “security”; and
(B) by striking “pilot”;
(2) in subsection (a)—
(A) by striking “Not later than 1 year after the date of enactment of this Act, the Director shall establish a ransomware vulnerability warning pilot program” and inserting “There is established in the Cybersecurity and Infrastructure Security Agency a security vulnerability warning program”; and
(B) by striking “associated with common ransomware attacks”;
(3) by striking “pilot” each place it appears;
(4) in subsection (b)(1), by striking “utilized in ransomware attacks and mitigation techniques” and inserting “for information systems, and mitigation techniques relating thereto”;
(5) in subsection (d), by striking “covered entities” and inserting “covered utilities”;
(6) in subsection (e)—
(A) by striking “No procedure” and inserting the following:
“(1) In general.—No procedure”; and
(B) by adding at the end the following new paragraphs:
“(2) Exemption from disclosure.—Information shared by a covered entity with respect to the program established under subsection (a) is exempt from disclosure under section 552(b)(3) of title 5, United States Code, and any provision of State, local, or Tribal freedom of information law, open government law, open meetings law, open records law, sunshine law, or similar law requiring disclosure of information or records.
“(3) Prohibited activity.—The Director may not disclose, retain, or use information shared by a covered entity with respect to the program established under subsection (a) unless such disclosure, retention, or use, as the case may be, is for a purpose specified in subsection (d)(5)(A) of section 105 of the Cybersecurity Information Sharing Act of 2015 (6 U.S.C. 1504).
“(4) Privacy.—The Director shall retain information shared by a covered entity with respect to the program established under subsection (a) in a manner that protects from unauthorized use or disclosure any of the following:
“(A) Any personal information that is of a specific individual and included in such retained information.
“(B) Any information that identifies a specific individual and is included in such retained information.”; and
(7) by striking subsection (g) and inserting the following new subsections:
“(g) Cyber Hygiene Services.—
“(1) Automatic enrollment.—As part of the program established under subsection (a), the Director shall automatically enroll in the applicable cyber hygiene services of the Cybersecurity and Infrastructure Security Agency each covered utility.
“(2) Disenrollment.—A covered utility enrolled in a cyber hygiene service pursuant to paragraph (1) may disenroll from such service by submitting to the Director notice of such disenrollment.
“(h) Incident Response.—As part of the program established under subsection (a), if the Director determines that a covered utility has been affected by a cyber incident, the Director shall utilize the incident response capabilities of the Cybersecurity and Infrastructure Security Agency to carry out on behalf of such utility a response to such incident, as appropriate.
“(i) Coordination.—In carrying out the program established under subsection (a), the Director shall coordinate with the Administrator of the Environmental Protection Agency.
“(j) Termination.—The program established under subsection (a) shall terminate on the date that is five years after the date of the enactment of this subsection.
“(k) Covered Utility Defined.—In this section, the term ‘covered utility’ means an entity that is any of the following:
“(1) A water or wastewater utility that serves not more than 100,000 individuals.
“(2) An eligible entity (as such term is defined in section 40124 of the Infrastructure Investment and Jobs Act (42 U.S.C. 18723)).
“(3) An operator of any of the following:
“(A) A public water system (as such term is defined in section 1401 of the Safe Drinking Water Act (42 U.S.C. 300f)).
“(B) Treatment works (as such term is defined in section 212 of the Federal Water Pollution Control Act (33 U.S.C. 1292)).”. <all>
Comments